01 BASELINE RECEIVERNO SOURCE CHECK
EO / CAM 07● REC
RECEIVER STATUSFEED ACCEPTEDREPLAY NOT IDENTIFIED
TRANSPORT STATUS // RECEIVEDSOURCE UNVERIFIED
TRUST INFRASTRUCTURE FOR CONTESTED SYSTEMS
A secure connection does not prove the source. 4MIK binds verifiable evidence to data where it begins, so receiving systems can check what they are trusting before they act.
THE PROBLEM / 01
The next attack does not have to break encryption. It can target the information your systems trust before that information ever reaches the encrypted link.
Replayed video. Fabricated telemetry. Impersonated sources. Machine actions executed outside their authority. As decision cycles accelerate, verification has to move closer to the source—and into the decision path.
SEE WHAT CHANGES WITH 4MIK ↗Illustration of a general threat model, not a claim that every system behaves this way.
SEE THE DIFFERENCE / 02
What a receiving system does with a feed can change when it verifies source-bound evidence instead of simply accepting the incoming video.
CONCEPT DEMONSTRATION ONLY. This interaction illustrates an expected verification outcome under defined conditions; it is not live sensor data or a measured product result. The source artwork is synthetic.
THE APPROACH / 03
4MIK adds an evidence and verification layer to the systems that generate, transmit, consume, and act on machine data.
Associate data with verifiable cryptographic evidence from the originating identity.
Check provenance, integrity, freshness, and continuity at the receiving boundary.
Give the consuming application a meaningful verification result before consequential action.
THE 4MIK CONTROL ARCHITECTURE / 04
E5 is the governing control architecture across the 4MIK stack. It defines the sequence by which identity is established, evidence is attached, policy is enforced, invalid inputs are rejected, and machine action is allowed only when trust conditions are satisfied.
CONTROL SEQUENCE
Rather than assuming a source should be trusted, E5 creates a repeatable decision sequence: establish identity, protect and bind integrity, apply policy, reject what fails, and execute only when the evidence supports action.
Establish verifiable identity for authorized participants and sources.
Protect data and bind integrity to source.
Apply authority and policy before action.
Reject unauthorized sources, altered data, stale state, replay, and invalid requests.
Allow action only when identity, integrity, freshness, continuity, and authority are verified.
WHERE IT MATTERS / 05
Defense is the starting point. The underlying trust problem follows data into every system where machines are expected to decide and act.
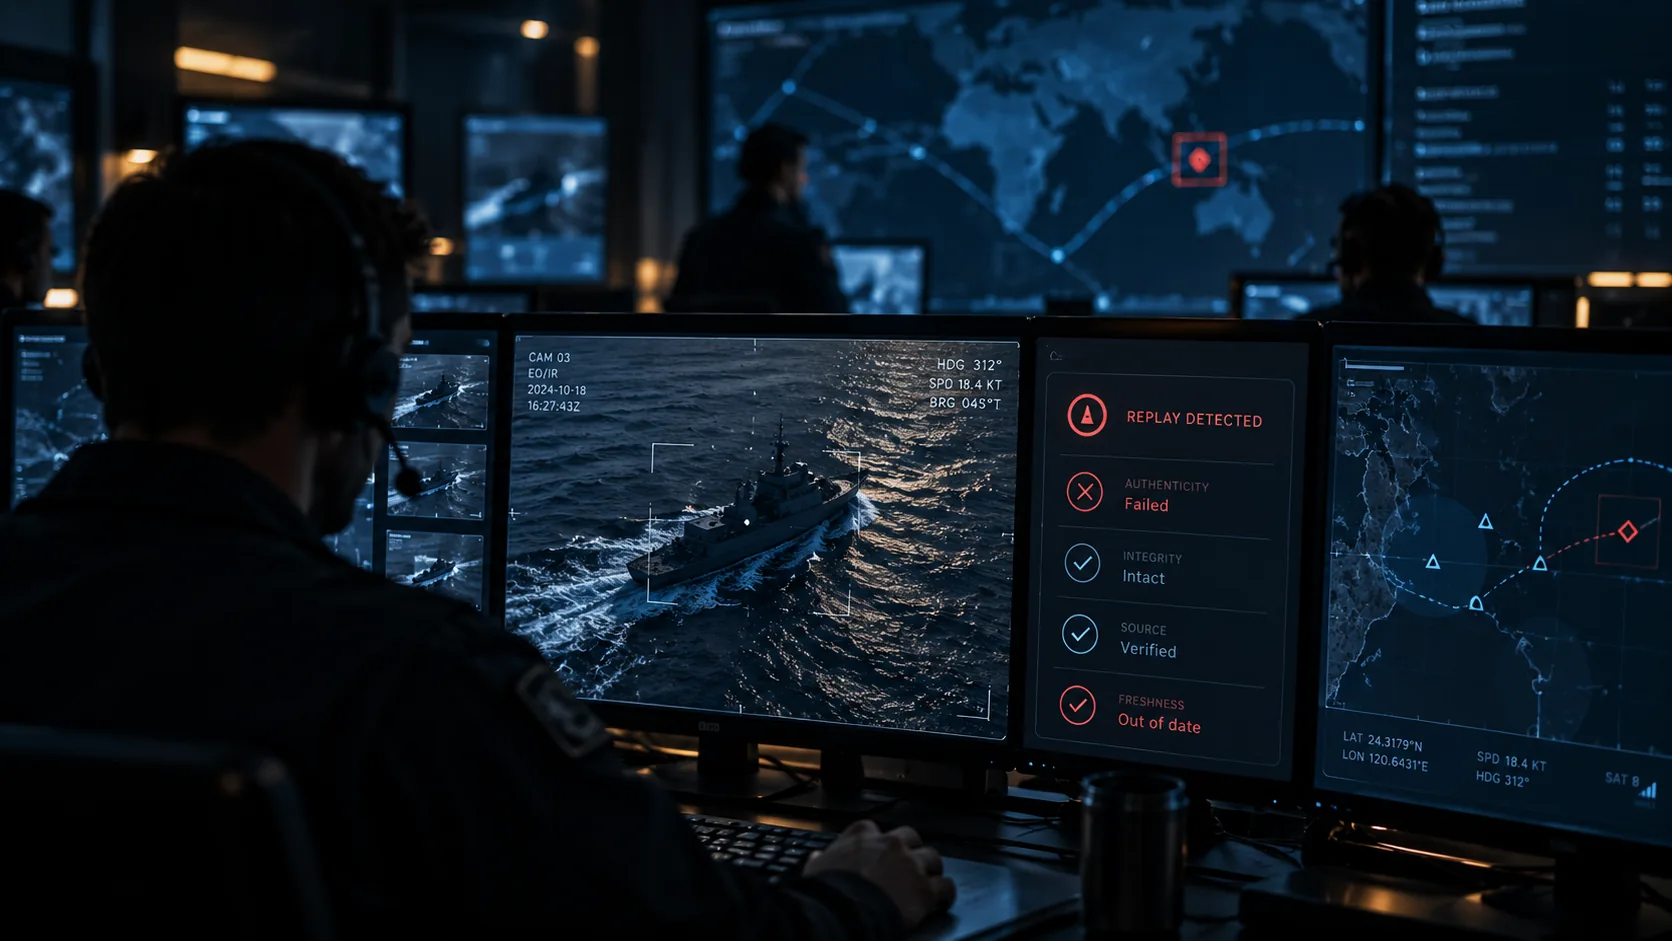
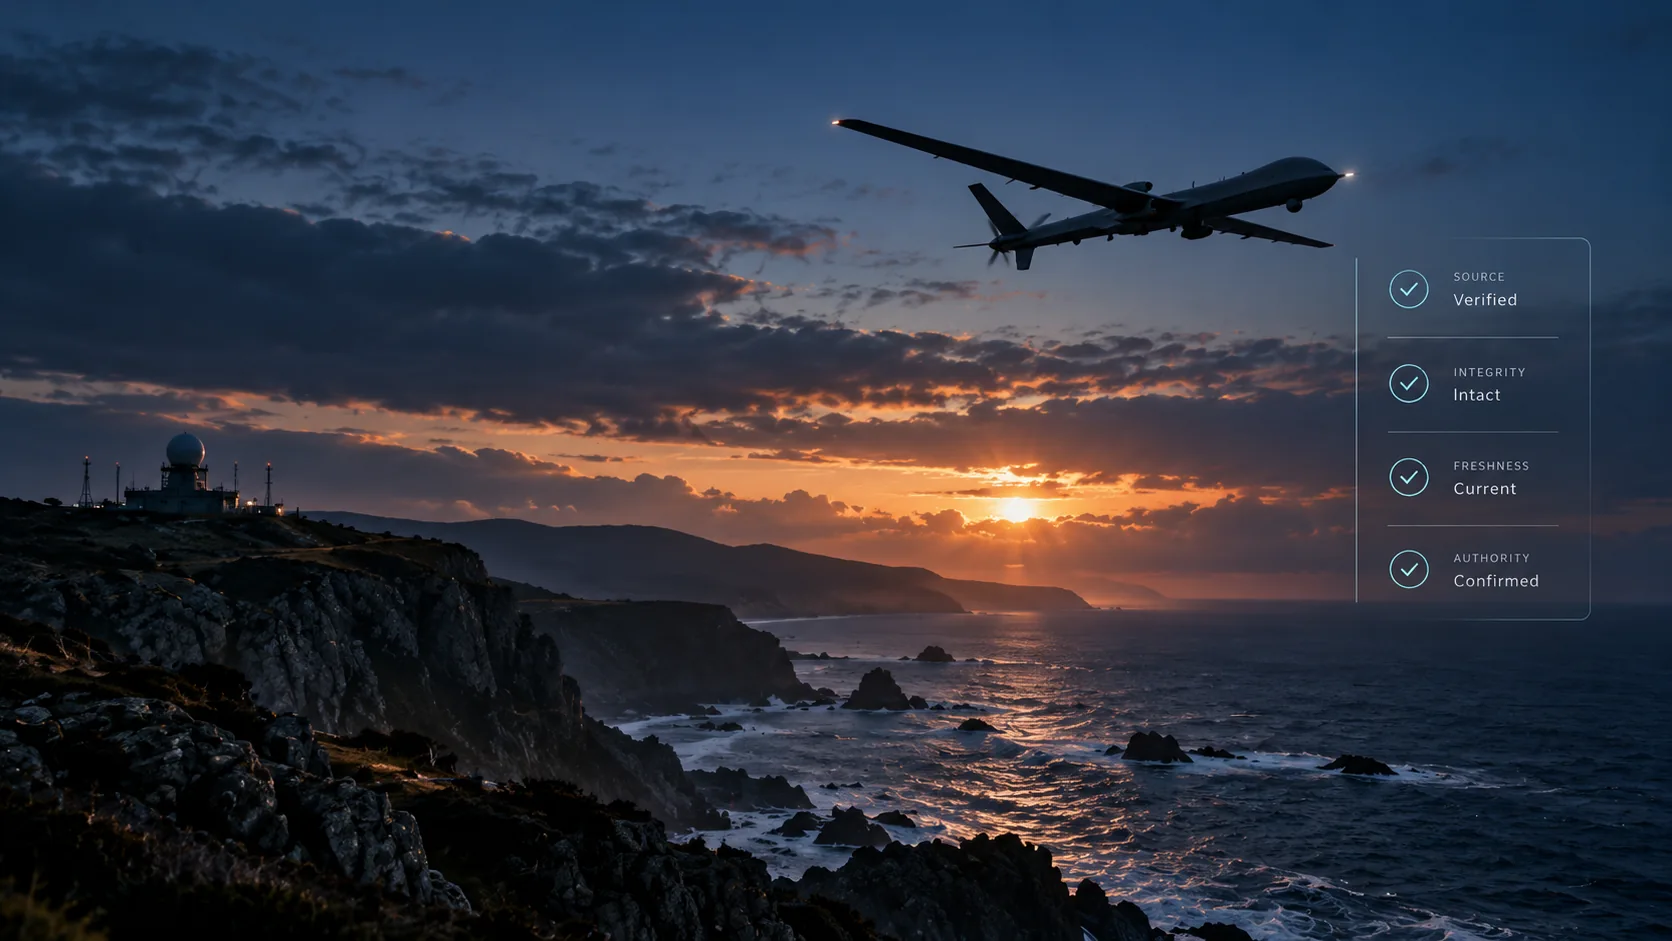
ISR, maritime, TAK/C2, distributed sensors
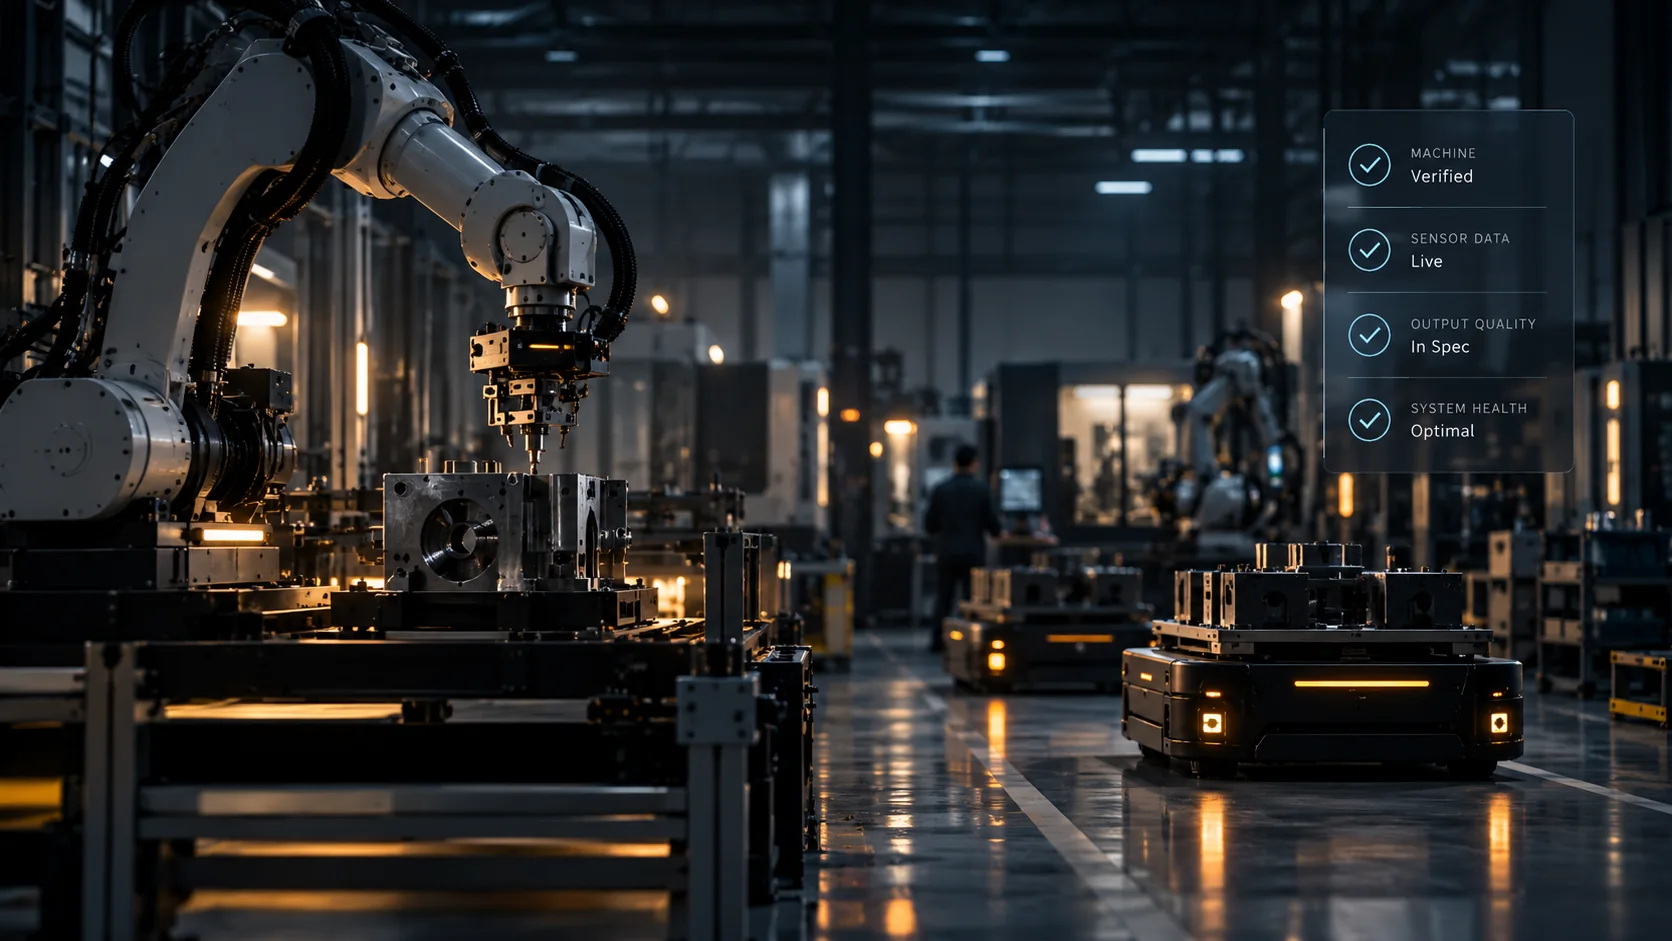
Factories, infrastructure, sensor networks
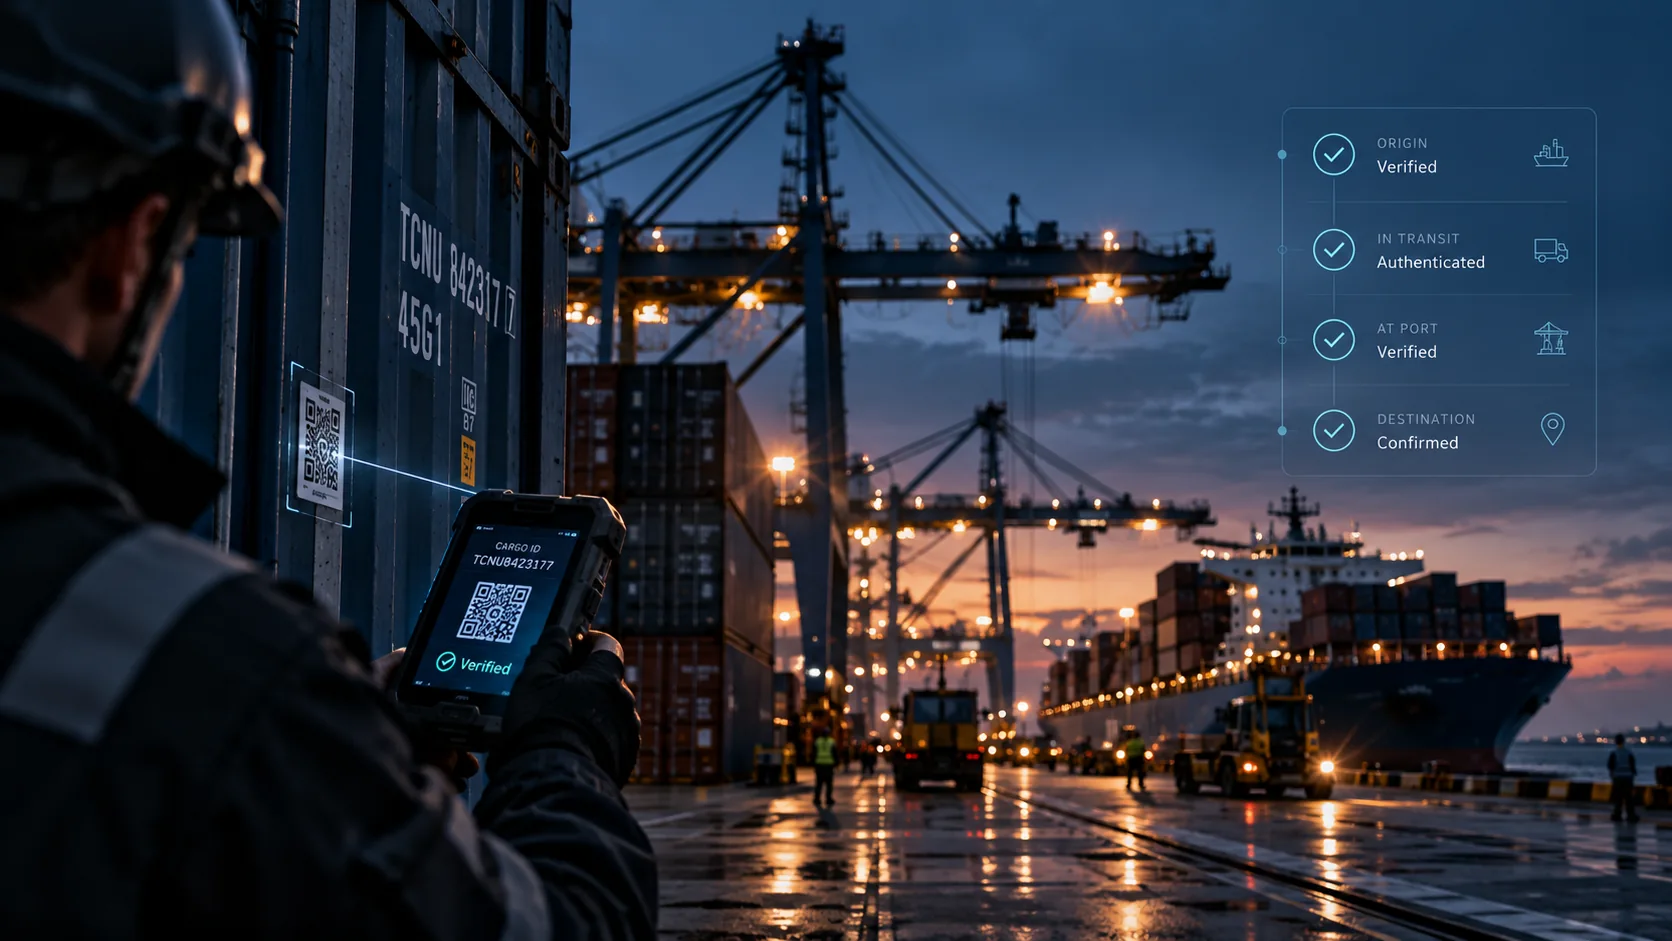
Ports, movement, operational telemetry
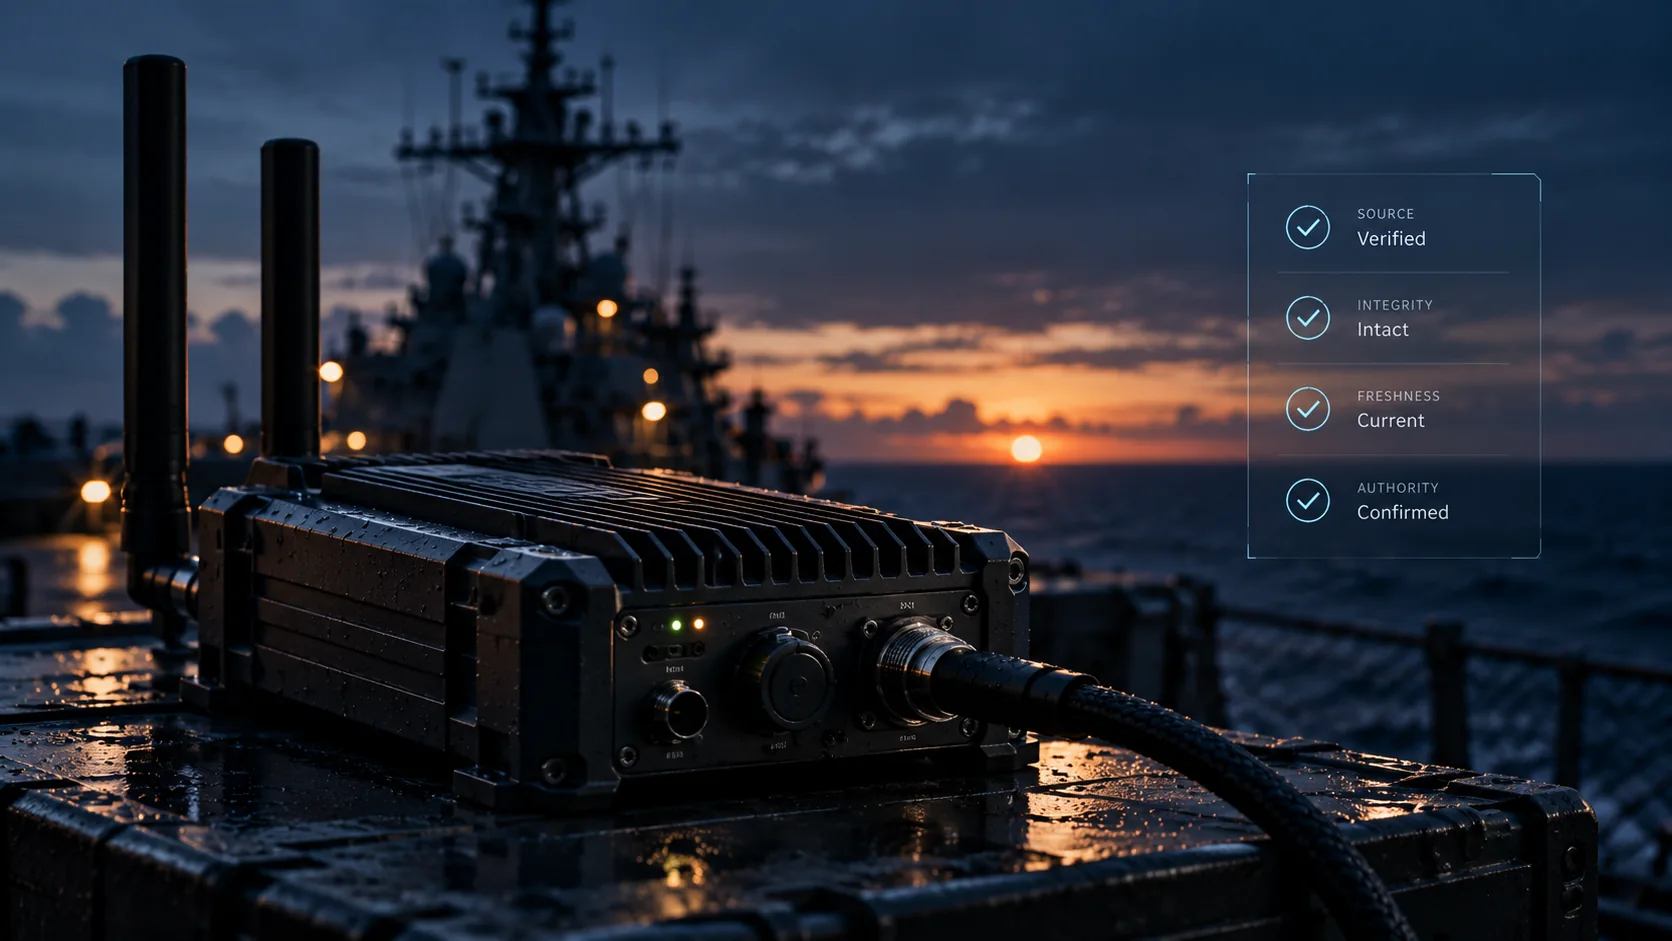 ILLUSTRATIVE EDGE SYSTEM
DESIGNED TO INTEGRATE / 06
An additive layer beneath mission applications: 4MIK is designed to help existing systems decide what information and which machine actions they can trust.
DISCUSS AN INTEGRATION ↗4MIK / THE NEXT TRUST STANDARD
See how verifiable source identity and evidence can change decisions inside your system.
START A TECHNICAL CONVERSATION ↗